Archive

October 22, 2026

Browsing

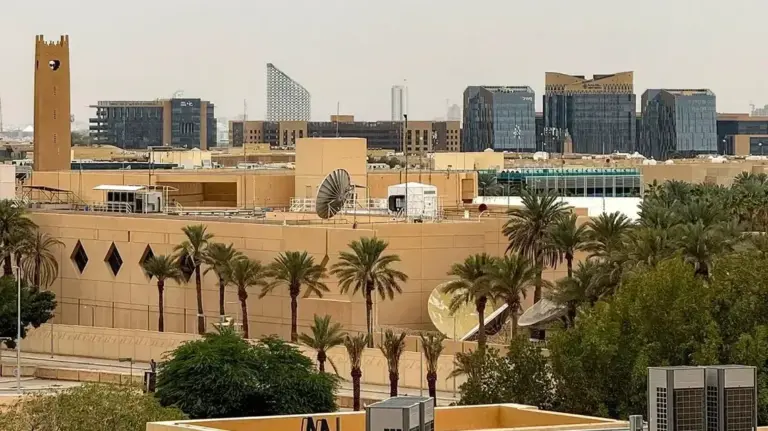
The Trump administration has ordered non-emergency U.S. government employees and their families to leave Saudi Arabia as deadly Houthi attacks intensify across the kingdom, raising the stakes as President Donald Trump weighs direct military action against the Iran-backed group.

State Department spokesperson Tommy Pigott confirmed Wednesday that the mandatory departure order applies only to Saudi Arabia, pushing back on reports that Washington was preparing a broader evacuation of diplomatic personnel across the Gulf.

“The U.S. Department of State issued an ordered departure for non-emergency U.S. government employees and their family members in Saudi Arabia only,” Pigott said.

HOW SAUDI ARABIA’S DEFENSE VULNERABILITIES COULD BECOME TRUMP’S PROBLEM AMID HOUTHI ONSLAUGHT

The order comes amid a surge in Houthi missile and drone attacks that has left civilians dead, disrupted air travel and sent Saudi Arabia scrambling for additional missile defenses.

“Iranian-supported Houthis have increasingly engaged in hostilities against Saudi Arabia, including attacks on civilian airports and other critical infrastructure resulting in civilian casualties and severe travel disruptions,” Pigott added.

President Donald Trump is weighing whether to launch direct U.S. military strikes against the Houthis, whose expanding missile and drone campaign has increasingly threatened Saudi cities, airports and energy infrastructure.

Houthi strikes and attempted strikes on Saudi Arabia more than doubled in a single week this month, according to the Armed Conflict Location & Event Data Project, with airports in Riyadh, Jizan, Najran, Dammam and Abha targeted since Oct. 5.

The deadliest barrage struck King Khalid International Airport in Riyadh, killing at least 13 people and wounding more than 300.

SAUDI ARABIA ON EDGE: ICONIC KINGDOM CENTRE SENDS WORKERS HOME AMID HOUTHI ATTACKS

The escalating attacks have prompted Saudi Arabia to seek additional military support from its allies. Britain announced Tuesday that it would deploy Typhoon fighter jets to help defend Saudi cities and critical infrastructure, while Egypt is assisting the kingdom and Israel has offered to help.

Riyadh has also asked Washington for additional missile interceptors, though U.S. officials have warned that global demand is straining available supplies.

“I also talked to Saudi Arabia today; they’d like interceptors. Israel would like interceptors. We would like interceptors. Every country in the world would like interceptors,” Secretary of State Marco Rubio said Tuesday.

Rubio described the weapons as “probably the most in-demand product right now in the defense field,” acknowledging that the United States must balance requests from allies against its own military requirements.

The growing threat has exposed the difficulty of defending Saudi Arabia’s vast territory against relatively inexpensive missiles and drones, even with some of the world’s most sophisticated air defenses.

“Saudi Arabia is a huge geography to protect, and this speaks to a larger threat we’re facing globally: a relatively small nonstate actor can pose a serious challenge to even a sophisticated and extremely expensive military,” Farea Al-Muslimi, a research fellow at Chatham House, told Fox News Digital in an interview published Wednesday.

“The Houthis can impose enormous costs without having to spend very much themselves,” he said.

Trump has left open the possibility of direct military intervention against the Houthis, telling reporters earlier this month that the U.S. could join Saudi strikes against the group.

“We may. We’re gonna look at it,” Trump said. “We’ll make a decision. We move very quickly.”

SIGN UP TO GET THE POLITICS NEWSLETTER

The U.S. conducted a roughly two-month bombing campaign against Houthi targets in Yemen in 2025 before Trump halted the operation following an Oman-brokered agreement.

The U.S. continues to provide intelligence and targeting support to Saudi Arabia as Trump weighs whether to launch another round of strikes against the Houthis.
Democrats are up in arms after a so-called polling firm that projected far-left candidates as strong contenders in several primaries admitted that it had fabricated its polling data.

Wedgewood Polling, which billed itself as an election survey company, released a statement Tuesday night admitting it used “fabricated numbers” for an “experimental project to demonstrate the vulnerabilities, lack of oversight, and overall low barrier to entry in the modern political polling industry.”

The group’s polls were cited by Abdul El-Sayed’s campaign amid a high-profile primary race against Michigan state Sen. Mallory McMorrow and U.S. Rep. Haley Stevens, D-Mich. The nonpartisan polling aggregator Political Polls also cited Wedgewood in the Wisconsin gubernatorial race, showing socialist Francesca Hong having an edge over Republican candidate Rep. Tom Tiffany, R-Wis.

McMorrow said Wedgewood’s numbers led to her donations drying up and reporters having “hounded” her with calls to drop out of the race.

JONATHAN TURLEY: FAKE POLLSTER’S STUNT WAS A RECKLESS GAME WITH REAL RACES

“Sure, a point was proven. Polling is broken. But tens of thousands of people poured their hearts, time, energy, hard-earned money into something they believed in – for a year-and-a-half, and it was treated like a game,” she said in a statement on X. “Trust is already at an all-time low. We don’t get out of this mess without rebuilding trust. And media – who loves to ride the drama of a pollercoaster – needs to take a hard look at what’s legitimate and what’s not.”

Unlike El-Sayed, who advanced from Michigan’s Democratic Senate primary, Hong lost Wisconsin’s Democratic gubernatorial primary to the establishment-backed candidate. El-Sayed, a former Michigan public health official, is currently locked in a tight race against former U.S. Rep. Mike Rogers, R-Mich., for Michigan’s open Senate seat.

Democrat strategist Jennifer Holdsworth said she ran a super PAC that raised money for McMorrow and that “this poll was used by several donors to pull back funding at a time we were being outspent by $80 million.”

MORNING GLORY: THE POLLS GOT MICHIGAN BADLY WRONG. NOW DEMOCRATS MAY FACE A BIGGER RECKONING

Wedgewood’s numbers were cited by high-profile outlets like The New York Times and Decision Desk HQ, which both said they have since removed them from their projections.

The Times said it removed 15 polls released by Wedgewood between June and October after it admitted to fabricating data. The outlet said Wedgewood had “answered a series of questions regarding the identities of the pollsters; the methods they were using to draw their sample, contact respondents and weight their polls; and the source of their funding” during its vetting process.

Decision Desk HQ said it removed 17 Wedgewood polls from its projections but that it “has not changed the projected seat totals or chamber control probabilities in the Senate or House.”

Wedgewood Polling’s statement said it “was never intended to sway an election” but rather was aimed as a “wake-up call” about data integrity and vetting standards.

MYSTERIOUS POLLING FIRM BEHIND FAKE ELECTION SURVEYS CLOSES AFTER ADMITTING ‘SOCIAL EXPERIMENT’

“These people are absolute scumbags,” veteran Democratic strategist and former Kamala Harris advisor Mike Nellis told Fox News Digital. “They can try to claim that they have some moral high ground here, but they lied about their polling data, got caught, and are freaking out because they’ve committed fraud.”

“The people responsible for this should be run out of American politics, and if they can be, they should be prosecuted to the full extent of the law,” Nellis said. He added that both Democrats and Republicans, as well as the media, should reflect on how polling is verified “because there’s likely other people that are doing things like this.”

TOP ELECTION SCHEMES ROILING KEY MIDTERM RACES AS BOTH PARTIES ACCUSE RIVALS OF TRICKERY

Independent outlet FiftyPlusOne said it was investigating Wedgewood when it had released its statement. Co-founder G. Elliott Morris wrote on X, “We were investigating Wedgewood for faking their data and emailed them for comment this morning, ahead of publishing the findings tomorrow. They are trying to cover up their fraud with the ‘we were doing a social experiment’ excuse.”

Former Obama staffer Tommy Vietor said on X that Wedgewood’s actions amounted to “lying and fraud.”

A group called “Wedgewood Polls” had also previously created a GoFundMe to raise money for polling in Nebraska’s gubernatorial and Senate races. It raised $500 of its intended $5,000.

“I know they crowdfunded, I believe, a good chunk of their polls,” Nellis told Fox News Digital. “Are they going to return that money? And if not, are they going to be prosecuted?”

FOX NEWS POLL: IT’S A LONE STAR SENATE SHOWDOWN BETWEEN TALARICO AND PAXTON

Other Wedgewood surveys showed Democrats with significant edges over Republicans in states like Texas, where a July Wedgewood poll showed James Talarico leading state Attorney General Ken Paxton among Hispanics by 64% to 30%.

Republicans, including President Donald Trump, have long heaped doubt on the veracity of polls.

Polls notably showed former Secretary of State Hillary Clinton with an edge over Trump in 2016 — far from the actual result.

And with the fight for control of Congress coming to a head in November, every data point is being scrutinized as political tea leaves.

Fox News Digital reached out to McMorrow’s state Senate office, Stevens’ campaign and strategist Lis Smith for further comment.

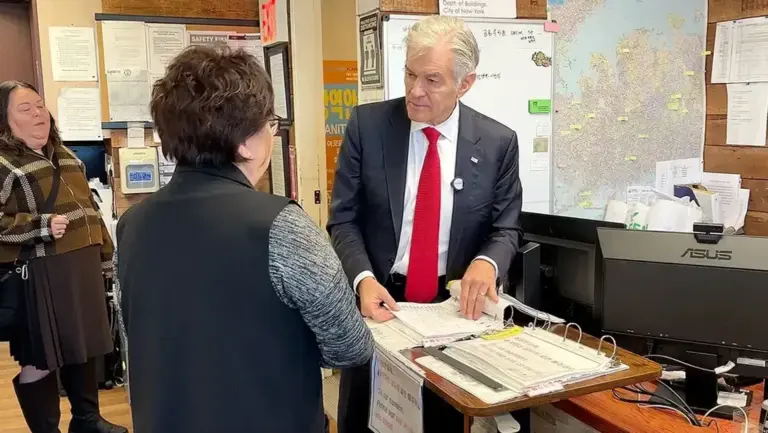
FIRST ON FOX: Centers for Medicare & Medicaid Services Administrator Dr. Mehmet Oz is taking Americans inside the Trump administration’s war on healthcare fraud in a new documentary highlighting massive Medicare schemes, suspected hospice scams and allegations of organized crime involvement.

The 27-minute film, “War on Fraud,” first obtained by Fox News Digital, follows Oz across the country as he spotlights alleged fraud schemes targeting taxpayer-funded health care programs and details the administration’s efforts to crack down on those responsible.

“All these programs come back to one basic issue: Fraudsters and criminals don’t give a s— about you. They want your money, and they will walk all over your health, sacrifice your life and betray society’s trust to get your hard-earned money,” said Oz in the video. 

The documentary follows Oz across the country as he investigates suspected fraud involving Medicare, Medicaid, hospice care and other programs, with appearances from HHS Secretary Robert F. Kennedy Jr. and CMS Deputy Administrator Kim Brandt.

DR OZ SAYS 800 HOSPICE PROVIDERS SUSPENDED IN CALIFORNIA OVER ALLEGED $1B MEDICARE FRAUD SCHEME

Fox News Digital accompanied Oz Tuesday as he confronted workers at New York City senior day care centers suspected of questionable Medicaid billing practices during a sweeping federal fraud investigation.

More than 80 New York City providers received warning letters from CMS over questionable billing practices as part of a broader operation involving the FBI, HHS-OIG, NYPD and other agencies.

“FBI New York, along with multiple other law enforcement agencies are conducting law enforcement activity in the area of Queens, Staten Island, Brooklyn and other locations around New York City in connection with ongoing federal investigations,” an FBI spokesperson said of the crackdown. 

ON THE STREETS WITH DR OZ AS SURPRISE FRAUD CRACKDOWN SENDS DAYCARE DIRECTORS SCRAMBLING

Oz flagged what he described as a series of irregularities, including low attendance despite high Medicaid billing, questionable wheelchair transportation charges, seniors entering without signing in, inconsistent attendance claims and sign-in sheets containing future-dated entries.

The crackdown comes as CMS is pulling back the curtain on its broader war on fraud, releasing a new documentary that takes viewers inside the agency’s efforts to track down schemes siphoning taxpayer dollars from America’s healthcare programs.

In one segment of the film, Oz highlights hospice care as a hotbed for potential fraud, pointing to the Los Angeles area, where he says roughly 2,000 hospice providers operate, a concentration he argues has raised serious concerns about fraudulent billing.

FBI ADDS 2 FUGITIVES TO ‘MOST WANTED FRAUDSTERS’ LIST AMID HISTORIC $6.5B HEALTHCARE TAKEDOWN: PATEL

Oz claims in the documentary that Russian organized crime groups are involved in some suspected hospice fraud operations, alleging that unsuspecting patients are being enrolled in hospice care under false pretenses.

He claims the schemes involve falsely declaring patients terminally ill and misleading them into enrolling in hospice care, potentially limiting their access to treatment for conditions classified as terminal while allowing fraudulent operators to bill Medicare for services under false pretenses.

Minnesota has become a major focus of the Trump administration’s broader crackdown on government benefits fraud following a series of high-profile scandals involving taxpayer-funded programs.

VANCE-LED TASK FORCE CUTS OFF $1.4B FROM HOME HEALTH, HOSPICE PROVIDERS SUSPECTED OF FRAUD

Oz said Minnesota’s $250 million “Feeding Our Future” scandal helped intensify the administration’s focus on large-scale fraud, pointing to a case that erupted into the national spotlight in 2022 and has since produced a wave of federal convictions.

The White House Task Force on Fraud, led by Vice President JD Vance, has joined Oz in a media blitz highlighting alleged scams as the administration ramps up its crackdown on corruption in taxpayer-funded programs.

The documentary highlights one of the largest alleged Medicare fraud schemes in U.S. history, involving $3.7 billion in fraudulent billing claims tied to medical equipment companies operating in Delray Beach, Florida, according to federal prosecutors.

Federal prosecutors allege the scheme involved billing for medical equipment patients never requested or needed, and the accused ringleader fled the U.S. before being captured in Turkey and returned to South Florida to face federal charges.

FBI BRINGS BACK FUGITIVE ACCUSED IN $3.7B MEDICARE FRAUD SCHEME AFTER CAPTURE IN TURKEY

The documentary also shows Oz during an earlier visit to Flushing, Queens, where he describes a cluster of businesses — including a social adult daycare center, pharmacy and medical center — as a “clubhouse for crooks,” alleging the businesses are part of a fraudulent billing operation.

Oz says they recruit seniors, get them in, game the system and they use their ID numbers to charge everybody, “which means they are charging you.”

The documentary will be released Wednesday at 4 P.M. ET on Oz’s X account.

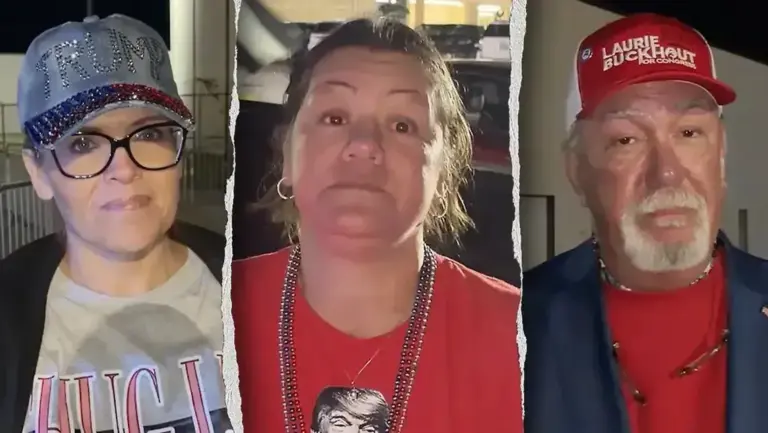
As gas prices climb amid the conflict with Iran, some of President Donald Trump’s most loyal supporters say they’re willing to pay more at the pump if it means keeping Tehran from obtaining a nuclear weapon — even with the midterm elections just two weeks away.

“If you’re really a good American, you’ll be thinking not for yourself or how much you’re spending for gas. But what life is going to be like for your children, your grandchildren and great-grandchildren,” one voter told Fox News Digital on Tuesday evening. 

“What will they grow up to? You have to keep those people in the political regime in Iran without a nuclear weapon. If we don’t do something now, isn’t that worth paying another dollar a gallon?” 

Fox News Digital spoke with several voters following Trump’s Tuesday rally at Pitt-Greenville Airport about rising gas prices, the upcoming midterm elections and the ongoing war with Iran, which has sent oil prices surging and added to Americans’ affordability concerns.

VOTERS PREPARE TO WEIGH-IN ON TRUMP’S ECONOMY AS COSTS CONTINUE TO SURGE

“Things haven’t changed much since Sleepy Joe,” another local voter, Shauna, told Fox News Digital about former President Joe Biden. “At least prices. … But [Trump is] doing the best he can with what he has. Because, you know, he’s not Congress. He can only pass so much.”

Another rallygoer told Fox News Digital that preventing Iran from acquiring a nuclear weapon was worth the cost of higher gas prices for American drivers.

TRUMP VOTERS SAY COSTS ARE CRUSHING THEIR WALLETS — BUT LOOK PAST PRESIDENT FOR BLAME

“We believed in what he [Trump] was saying and what he stood for,” local voter Michael told Fox News Digital. “And you hear people today saying, ‘Y’all wanted to get politicians out of Washington.’ … We got a businessman in. [He] never claimed to be a politician. He’s a businessman.

“Even with the gas prices up for what he’s done in Iran,” he added. “To me [that] is worth the high gas prices. I’ll take that any day to stop a country like Iran and take that nuclear power away. That’s a no-brainer, you know. Now, will the gas prices come down? Absolutely. They will come down because of what he’s done.”

IRAN ‘MISCALCULATING’ BY BETTING ON MIDTERMS AFTER 3-HOUR TALKS, TRUMP OFFICIALS WARN

Another Trump supporter, Steve, told Fox News Digital he would encourage other Americans to vote for GOP candidates despite high prices.

“It would take an act of God to lower prices before this election is over,” he said. “But I highly stress to everybody to vote Republican like you are voting like it’s the most important election in your lifetime. Because in many instances, it actually is.”

Trump has maintained that the ongoing war with Iran is a “small price to pay” to keep the nation safe.

The president has been crisscrossing the country in the final weeks before the Nov. 3 midterm elections, rallying his supporters in an effort to boost Republican candidates and help the GOP retain control of Congress. His North Carolina stop was aimed in part at bolstering Republican Senate candidate Michael Whatley, who is facing former Democratic Gov. Roy Cooper.

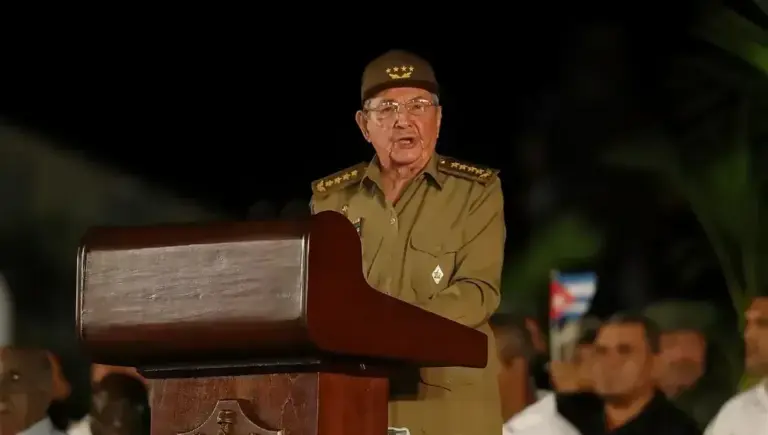
FIRST ON FOX: Cuban-American lawmakers are welcoming a Florida arrest warrant for former Cuban leader Raúl Castro over his alleged role in the 1996 shootdown of two civilian aircraft, saying the move marks a new step toward accountability for the communist regime and vowing to keep fighting for freedom on the island.

The warrant comes after Ariana Fajardo Orshan, chief judge of Florida’s 11th Judicial Circuit, found probable cause to believe Castro conspired to commit first-degree murder in connection with the shootdown of two Miami-based civilian aircraft involved in a humanitarian operation near Cuba in 1996.

“As the only Cuban-born member of Congress, this moment is deeply personal,” Rep. Carlos Giménez, R-Fla., told Fox News Digital. “For decades, Raúl Castro and his communist regime have oppressed the Cuban people while evading accountability.”

Giménez described the warrant as a “powerful message” in the “pursuit of justice,” adding that those responsible for the suffering of the Cuban people could soon “answer for their crimes.”

“No previous administration has taken this historic step, and our community is eternally grateful for it,” he continued. “For the millions of Cubans who have suffered under this tyranny, including those of us forced into exile, this represents a significant moment in our decades-long struggle for freedom.”

CUBAN AMERICAN LAWMAKERS WARN CUBA IS CLOSER THAN EVER TO REGIME CHANGE UNDER TRUMP ADMINISTRATION

Florida Attorney General James Uthmeier told Fox News Digital that Castro allegedly “ordered” the “premeditated, state-sanctioned murder of four Floridians in cold blood,” calling the warrant “a step toward accountability” for the conspiracy that led to the deaths of Carlos Costa, Pablo Morales, Mario de la Peña and Armando Alejandre Jr.

Uthmeier’s office said the warrant could limit Castro’s ability to travel to countries that have extradition agreements with the United States.

OBAMA’S BASEBALL OUTING WITH CASTRO REIGNITES FURY AFTER TRUMP DOJ DROPS HAMMER ON CUBAN LEADER

Giménez said that although the warrant is “historic,” he and other lawmakers will continue fighting until Cuba’s “political prisoners are released” and the “Cuban people can determine their own destiny.”

Florida state Rep. Juan Porras, another Cuban American lawmaker, said the warrant shows that Florida “will never forget” the victims of the communist regime’s atrocities.

CUBA’S DICTATORSHIP HAS LONG BEEN A THREAT TO AMERICA. NOW, IT’S FINALLY TEETERING

“Thank you to the Miami judge who signed a state arrest warrant for Raúl Castro for conspiracy to commit first-degree murder,” Porras told Fox News Digital. “Thirty years later, justice is still moving, but the work is not done. Cuba is not free yet, and we will not stop until it is.”

“Cuba will be free,” Porras added in Spanish.

The warrant stems from the Feb. 24, 1996, shootdown of two unarmed aircraft operated by Brothers to the Rescue over international waters. Four people were killed in the attack. Castro, who was Cuba’s defense minister at the time, was federally indicted earlier this year in connection with the deaths.

Web administrators and security teams worldwide are currently racing against time following the discovery of two critical vulnerabilities in PHP, a cornerstone of modern internet architecture. The flaws, identified as CVE-2026-109618 and CVE-2026-109619, effectively leave the digital front doors of millions of servers unlocked. Because PHP powers everything from global e-commerce giants like Magento to massive publishing platforms such as WordPress and Drupal, the potential for widespread devastation is immense. Experts warn that these gaps could allow unauthenticated attackers to seize remote control of systems or steal sensitive data including passwords and API keys.

The situation reached a fever pitch on Wednesday when the PHP Foundation released emergency patches, noting that there are no viable workarounds other than updating the software immediately. The risk is compounded by the sheer age of some existing infrastructure; while official support now only extends to version 8.2 and newer, many legacy systems dating back to 2004 remain active and forgotten in the corners of the web. This creates a massive surface area for what consultants describe as potentially wormable malware that could leap across large chunks of the internet with terrifying speed.

Panic set in even before the formal patches arrived, with several high profile entities taking drastic precautions. Government websites in Finland and France, along with portals for the Port of Rotterdam, were temporarily pulled offline to prevent exploitation. Industry observers note that the advent of artificial intelligence has further compressed the window for defense, as AI tools can help hackers weaponize such vulnerabilities almost instantly once they become public knowledge. Indeed, some security firms reported seeing early signs of attacks emerging moments after the flaw became known.

While agencies like those in Australia and the UK issued advance warnings urging organizations to audit their tech stacks, the urgency remains absolute. With a critical severity score of 9.2 out of 10, these bugs represent more than just a technical glitch; they are a systemic threat to how information moves online. For those managing web servers today, the message from the cybersecurity community is clear: every second spent delaying an update is an open invitation for a catastrophic breach.

Elon Musk has sent shockwaves through the investment community by suggesting that merging Tesla and SpaceX would be a good idea. During a recent earnings call for the aerospace giant, Musk revealed that special committees from both corporate boards have already begun discussing a potential tie-up. While he admitted that securing the necessary fifty percent shareholder approval for Tesla would be a high hurdle, he highlighted the immense synergy between the two firms in fields like artificial intelligence, chip design, and robotics. The prospect of a combined entity is bolstered by existing collaborations, including a joint semiconductor factory project in Texas involving Intel.

The timing of these comments is particularly striking as Musk prepares to report Tesla’s latest quarterly financial results. Wall Street analysts are currently eyeing an estimated revenue of twenty seven point nine billion dollars and earnings per share of forty three cents. Any dip below these marks could signal further trouble for the electric vehicle pioneer, which has struggled against fierce competition from Chinese rivals like BYD and Xiaomi. With vehicle deliveries recently slipping slightly compared to last year, investors are anxious to see if Tesla can reclaim its momentum amidst a challenging global economy and shifting tax credits.

Beyond the balance sheet, much of the anticipation surrounding Wednesday’s call centers on Musk’s pivot toward autonomy and robotics. Shareholders are eager for updates on the Cybercab and whether the Full Self Driving system will ever transition from supervised assistance to truly unsupervised automation. Despite facing stiff competition from Waymo in the United States and Apollo Go in China, Musk continues to bet heavily on robotaxis and humanoid robots. This shift is reflected in massive capital expenditures expected to exceed twenty five billion dollars this year as Tesla attempts to redefine itself as more than just a car company.

It has been a nightmare of a Wednesday for IT departments globally as a cascade of unrelated but severe security failures hit the internet almost simultaneously. The chaos began with government websites falling offline worldwide after artificial intelligence identified critical holes in PHP, a fundamental programming language used by millions of sites. The situation became so urgent that the U.S. National Security Agency issued a blunt warning to organizations to either update their systems immediately or shut them down entirely to avoid exploitation.

As technicians scrambled to fix those gaps, another wave of trouble arrived from Node.js, which revealed four high severity vulnerabilities in its latest release. Some of these flaws were particularly dangerous, potentially allowing attackers to run unauthorized code remotely or trick servers into bypassing essential identity verification checks. Meanwhile, users of LiteLLM found themselves in the crosshairs of a supply chain attack where malicious code was injected directly into popular registries like Docker Hub and PyPI, designed specifically to steal cloud credentials and passwords.

The instability extended even further into the foundations of web trust with the compromise of private keys at eMudhra, an Indian certificate authority. Because this allows hackers to impersonate legitimate websites with fraudulent certificates, some industry experts are already comparing the scale of the necessary cleanup to the infamous Heartbleed bug from years ago. This event capped off a brutal stretch for cybersecurity teams who have already been dealing with recent breaches at TiDB Cloud and exploits targeting Plex Media Servers and BeyondTrust products.

While these incidents aren’t connected by a single mastermind, their simultaneous occurrence underscores an escalating arms race in digital defense. Experts warn that as AI tools become more accessible, they will likely be used by attackers to find and weaponize vulnerabilities faster than humans can patch them. For now, the prevailing mood among security professionals is one of exhaustion as they play a desperate game of catch up against an increasingly automated threat landscape.

The very foundation of the modern internet is facing a moment of reckoning after the National Security Agency issued a stark warning regarding two critical vulnerabilities discovered within PHP. As a server side language powering roughly seventy percent of all websites including millions of WordPress installations, PHP is essentially the invisible glue holding much of the digital world together. The flaws are so severe that federal authorities suggested any site unable to patch immediately should simply be taken offline to prevent attackers from infiltrating sensitive databases or file systems.

What makes this discovery particularly unsettling is that these security gaps have existed silently since 2004, lurking in every version of the language starting with version five. For twenty years, these holes remained undetected by human eyes and traditional scanners alike. However, the tide turned when artificial intelligence entered the fray. Through OpenAI’s Patch the Planet initiative and separate efforts by Google’s Wiz using advanced AI agents, these dormant vulnerabilities were finally dragged into the light.

This situation presents a strange paradox where AI acts as both the savior and the threat. While large language models allowed researchers to find and fix these errors before malicious actors could exploit them, those same tools now make attacking outdated systems significantly easier. Experts warn that AI can now automatically adapt exploits to fit various memory layouts and configurations, removing barriers that previously kept hackers at bay.

The race is now on for millions of website administrators to migrate to current versions of PHP, specifically version 8.5.12, as many older iterations are no longer officially supported. Because these flaws are inherent to the language rather than specific platforms like WordPress, users must coordinate directly with their hosting providers to secure their environments. With the blueprints for these attacks now public knowledge, the window for protection is closing rapidly across thirty three million vulnerable sites globally.

A wave of digital outages swept across the globe this week as governments and major organizations scrambled to protect themselves from two critical security holes in PHP, a programming language that serves as a foundation for a vast portion of the internet. The situation became so urgent that national security agencies in the United States, Finland, and the Netherlands advised organizations to take their entire websites offline if they could not immediately apply a newly released emergency patch. This precautionary blackout left everything from Finnish public services and the Dutch parliament’s website to various BBC program pages and parts of Wikipedia momentarily inaccessible.

What makes this crisis particularly striking is how the vulnerabilities were uncovered. Researchers at cybersecurity firms Wiz and Calif utilized advanced artificial intelligence tools provided through an OpenAI initiative to spot flaws that had remained hidden for over a decade. Experts describe these gaps as some of the most severe ever detected by AI, noting that they could give hackers a direct path into a server’s private files or databases without requiring any login credentials. Some estimates suggest that up to seventy percent of the web relies on PHP, meaning millions of sites ranging from small blogs to massive corporate portals were suddenly exposed.

The urgency reached a fever pitch when details about the flaw leaked onto social media, forcing the PHP Foundation to accelerate its official warning and repair schedule. Cybersecurity specialists warn that because PHP is often embedded deep within other software like WordPress or hosting platforms, many companies might not even realize their systems are at risk. With reports already surfacing of early attack attempts, experts are urging administrators not only to update their software but to scan their systems for evidence that intruders may have already slipped through the cracks during the window of exposure.