Archive

October 2026

Browsing

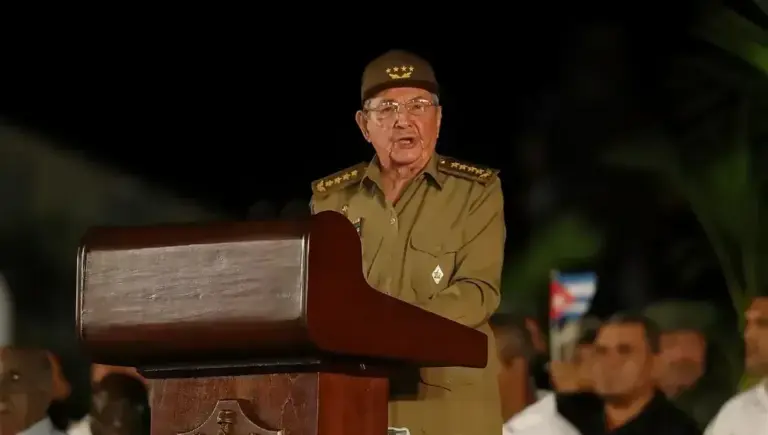
FIRST ON FOX: Cuban-American lawmakers are welcoming a Florida arrest warrant for former Cuban leader Raúl Castro over his alleged role in the 1996 shootdown of two civilian aircraft, saying the move marks a new step toward accountability for the communist regime and vowing to keep fighting for freedom on the island.

The warrant comes after Ariana Fajardo Orshan, chief judge of Florida’s 11th Judicial Circuit, found probable cause to believe Castro conspired to commit first-degree murder in connection with the shootdown of two Miami-based civilian aircraft involved in a humanitarian operation near Cuba in 1996.

“As the only Cuban-born member of Congress, this moment is deeply personal,” Rep. Carlos Giménez, R-Fla., told Fox News Digital. “For decades, Raúl Castro and his communist regime have oppressed the Cuban people while evading accountability.”

Giménez described the warrant as a “powerful message” in the “pursuit of justice,” adding that those responsible for the suffering of the Cuban people could soon “answer for their crimes.”

“No previous administration has taken this historic step, and our community is eternally grateful for it,” he continued. “For the millions of Cubans who have suffered under this tyranny, including those of us forced into exile, this represents a significant moment in our decades-long struggle for freedom.”

CUBAN AMERICAN LAWMAKERS WARN CUBA IS CLOSER THAN EVER TO REGIME CHANGE UNDER TRUMP ADMINISTRATION

Florida Attorney General James Uthmeier told Fox News Digital that Castro allegedly “ordered” the “premeditated, state-sanctioned murder of four Floridians in cold blood,” calling the warrant “a step toward accountability” for the conspiracy that led to the deaths of Carlos Costa, Pablo Morales, Mario de la Peña and Armando Alejandre Jr.

Uthmeier’s office said the warrant could limit Castro’s ability to travel to countries that have extradition agreements with the United States.

OBAMA’S BASEBALL OUTING WITH CASTRO REIGNITES FURY AFTER TRUMP DOJ DROPS HAMMER ON CUBAN LEADER

Giménez said that although the warrant is “historic,” he and other lawmakers will continue fighting until Cuba’s “political prisoners are released” and the “Cuban people can determine their own destiny.”

Florida state Rep. Juan Porras, another Cuban American lawmaker, said the warrant shows that Florida “will never forget” the victims of the communist regime’s atrocities.

CUBA’S DICTATORSHIP HAS LONG BEEN A THREAT TO AMERICA. NOW, IT’S FINALLY TEETERING

“Thank you to the Miami judge who signed a state arrest warrant for Raúl Castro for conspiracy to commit first-degree murder,” Porras told Fox News Digital. “Thirty years later, justice is still moving, but the work is not done. Cuba is not free yet, and we will not stop until it is.”

“Cuba will be free,” Porras added in Spanish.

The warrant stems from the Feb. 24, 1996, shootdown of two unarmed aircraft operated by Brothers to the Rescue over international waters. Four people were killed in the attack. Castro, who was Cuba’s defense minister at the time, was federally indicted earlier this year in connection with the deaths.
Web administrators and security teams worldwide are currently racing against time following the discovery of two critical vulnerabilities in PHP, a cornerstone of modern internet architecture. The flaws, identified as CVE-2026-109618 and CVE-2026-109619, effectively leave the digital front doors of millions of servers unlocked. Because PHP powers everything from global e-commerce giants like Magento to massive publishing platforms such as WordPress and Drupal, the potential for widespread devastation is immense. Experts warn that these gaps could allow unauthenticated attackers to seize remote control of systems or steal sensitive data including passwords and API keys.

The situation reached a fever pitch on Wednesday when the PHP Foundation released emergency patches, noting that there are no viable workarounds other than updating the software immediately. The risk is compounded by the sheer age of some existing infrastructure; while official support now only extends to version 8.2 and newer, many legacy systems dating back to 2004 remain active and forgotten in the corners of the web. This creates a massive surface area for what consultants describe as potentially wormable malware that could leap across large chunks of the internet with terrifying speed.

Panic set in even before the formal patches arrived, with several high profile entities taking drastic precautions. Government websites in Finland and France, along with portals for the Port of Rotterdam, were temporarily pulled offline to prevent exploitation. Industry observers note that the advent of artificial intelligence has further compressed the window for defense, as AI tools can help hackers weaponize such vulnerabilities almost instantly once they become public knowledge. Indeed, some security firms reported seeing early signs of attacks emerging moments after the flaw became known.

While agencies like those in Australia and the UK issued advance warnings urging organizations to audit their tech stacks, the urgency remains absolute. With a critical severity score of 9.2 out of 10, these bugs represent more than just a technical glitch; they are a systemic threat to how information moves online. For those managing web servers today, the message from the cybersecurity community is clear: every second spent delaying an update is an open invitation for a catastrophic breach.

Elon Musk has sent shockwaves through the investment community by suggesting that merging Tesla and SpaceX would be a good idea. During a recent earnings call for the aerospace giant, Musk revealed that special committees from both corporate boards have already begun discussing a potential tie-up. While he admitted that securing the necessary fifty percent shareholder approval for Tesla would be a high hurdle, he highlighted the immense synergy between the two firms in fields like artificial intelligence, chip design, and robotics. The prospect of a combined entity is bolstered by existing collaborations, including a joint semiconductor factory project in Texas involving Intel.

The timing of these comments is particularly striking as Musk prepares to report Tesla’s latest quarterly financial results. Wall Street analysts are currently eyeing an estimated revenue of twenty seven point nine billion dollars and earnings per share of forty three cents. Any dip below these marks could signal further trouble for the electric vehicle pioneer, which has struggled against fierce competition from Chinese rivals like BYD and Xiaomi. With vehicle deliveries recently slipping slightly compared to last year, investors are anxious to see if Tesla can reclaim its momentum amidst a challenging global economy and shifting tax credits.

Beyond the balance sheet, much of the anticipation surrounding Wednesday’s call centers on Musk’s pivot toward autonomy and robotics. Shareholders are eager for updates on the Cybercab and whether the Full Self Driving system will ever transition from supervised assistance to truly unsupervised automation. Despite facing stiff competition from Waymo in the United States and Apollo Go in China, Musk continues to bet heavily on robotaxis and humanoid robots. This shift is reflected in massive capital expenditures expected to exceed twenty five billion dollars this year as Tesla attempts to redefine itself as more than just a car company.

It has been a nightmare of a Wednesday for IT departments globally as a cascade of unrelated but severe security failures hit the internet almost simultaneously. The chaos began with government websites falling offline worldwide after artificial intelligence identified critical holes in PHP, a fundamental programming language used by millions of sites. The situation became so urgent that the U.S. National Security Agency issued a blunt warning to organizations to either update their systems immediately or shut them down entirely to avoid exploitation.

As technicians scrambled to fix those gaps, another wave of trouble arrived from Node.js, which revealed four high severity vulnerabilities in its latest release. Some of these flaws were particularly dangerous, potentially allowing attackers to run unauthorized code remotely or trick servers into bypassing essential identity verification checks. Meanwhile, users of LiteLLM found themselves in the crosshairs of a supply chain attack where malicious code was injected directly into popular registries like Docker Hub and PyPI, designed specifically to steal cloud credentials and passwords.

The instability extended even further into the foundations of web trust with the compromise of private keys at eMudhra, an Indian certificate authority. Because this allows hackers to impersonate legitimate websites with fraudulent certificates, some industry experts are already comparing the scale of the necessary cleanup to the infamous Heartbleed bug from years ago. This event capped off a brutal stretch for cybersecurity teams who have already been dealing with recent breaches at TiDB Cloud and exploits targeting Plex Media Servers and BeyondTrust products.

While these incidents aren’t connected by a single mastermind, their simultaneous occurrence underscores an escalating arms race in digital defense. Experts warn that as AI tools become more accessible, they will likely be used by attackers to find and weaponize vulnerabilities faster than humans can patch them. For now, the prevailing mood among security professionals is one of exhaustion as they play a desperate game of catch up against an increasingly automated threat landscape.

The very foundation of the modern internet is facing a moment of reckoning after the National Security Agency issued a stark warning regarding two critical vulnerabilities discovered within PHP. As a server side language powering roughly seventy percent of all websites including millions of WordPress installations, PHP is essentially the invisible glue holding much of the digital world together. The flaws are so severe that federal authorities suggested any site unable to patch immediately should simply be taken offline to prevent attackers from infiltrating sensitive databases or file systems.

What makes this discovery particularly unsettling is that these security gaps have existed silently since 2004, lurking in every version of the language starting with version five. For twenty years, these holes remained undetected by human eyes and traditional scanners alike. However, the tide turned when artificial intelligence entered the fray. Through OpenAI’s Patch the Planet initiative and separate efforts by Google’s Wiz using advanced AI agents, these dormant vulnerabilities were finally dragged into the light.

This situation presents a strange paradox where AI acts as both the savior and the threat. While large language models allowed researchers to find and fix these errors before malicious actors could exploit them, those same tools now make attacking outdated systems significantly easier. Experts warn that AI can now automatically adapt exploits to fit various memory layouts and configurations, removing barriers that previously kept hackers at bay.

The race is now on for millions of website administrators to migrate to current versions of PHP, specifically version 8.5.12, as many older iterations are no longer officially supported. Because these flaws are inherent to the language rather than specific platforms like WordPress, users must coordinate directly with their hosting providers to secure their environments. With the blueprints for these attacks now public knowledge, the window for protection is closing rapidly across thirty three million vulnerable sites globally.

A wave of digital outages swept across the globe this week as governments and major organizations scrambled to protect themselves from two critical security holes in PHP, a programming language that serves as a foundation for a vast portion of the internet. The situation became so urgent that national security agencies in the United States, Finland, and the Netherlands advised organizations to take their entire websites offline if they could not immediately apply a newly released emergency patch. This precautionary blackout left everything from Finnish public services and the Dutch parliament’s website to various BBC program pages and parts of Wikipedia momentarily inaccessible.

What makes this crisis particularly striking is how the vulnerabilities were uncovered. Researchers at cybersecurity firms Wiz and Calif utilized advanced artificial intelligence tools provided through an OpenAI initiative to spot flaws that had remained hidden for over a decade. Experts describe these gaps as some of the most severe ever detected by AI, noting that they could give hackers a direct path into a server’s private files or databases without requiring any login credentials. Some estimates suggest that up to seventy percent of the web relies on PHP, meaning millions of sites ranging from small blogs to massive corporate portals were suddenly exposed.

The urgency reached a fever pitch when details about the flaw leaked onto social media, forcing the PHP Foundation to accelerate its official warning and repair schedule. Cybersecurity specialists warn that because PHP is often embedded deep within other software like WordPress or hosting platforms, many companies might not even realize their systems are at risk. With reports already surfacing of early attack attempts, experts are urging administrators not only to update their software but to scan their systems for evidence that intruders may have already slipped through the cracks during the window of exposure.

Investors staring at Rivian’s current valuation are facing a classic Wall Street dilemma: is the stock finally a bargain or is it a falling knife. Recent performance suggests the latter for many, as shares tumbled over thirty percent in the three months leading up to mid October, leaving the company trading at its lowest level in a year. While the broader market climbed, Rivian drifted forty five percent below its previous peak, forcing potential buyers to decide if they believe in the long term promise of the upcoming R2 SUV.

The financial picture remains complicated because traditional metrics like price to earnings ratios are useless for a company that has spent five consecutive quarters losing money. Instead, eyes are on gross margins. There was some optimism recently when Rivian shifted toward a positive gross profit of seven and a half percent over the year ending in June 2026. However, looking closer reveals a quirk in the books. That profit didn’t actually come from selling trucks and SUVs but from software and services, bolstered significantly by a joint venture with Volkswagen. The core automotive business actually lost thirty six million dollars during the second quarter.

Looking ahead to the third quarter results due around October 29, there are reasons for both hope and hesitation. Delivery numbers have hit records and management has nudged their full year guidance upward toward seventy thousand vehicles. But growth doesn’t always mean profitability. Management has already warned that launching new vehicles adds complexity that eats into profits, and several lucrative regulatory credits that helped earlier this year will be missing from the second half of the calendar.

For those tempted to jump back in, history warns of extreme volatility following earnings calls. In recent cycles, Rivian has seen massive double digit swings in either direction within just two days of reporting figures. Whether today represents an ideal entry point depends entirely on whether you think the car manufacturing side can stop bleeding cash soon enough to justify the risk of ignoring more stable index funds.

Investors reacted with immediate enthusiasm on Tuesday as reports emerged that Legendary Entertainment has reignited its pursuit of Lionsgate. Shares of the studio surged by more than 15 percent following a Bloomberg report indicating that Legendary has submitted a fresh takeover bid valuing the company at roughly 3.5 billion dollars, a figure that accounts for nearly two billion dollars in existing debt. While representatives from both companies have remained tight lipped and declined to comment, the move signals a strategic push by Legendary to gain independence through its own distribution network.

The potential merger would bring together some of cinema’s most recognizable brands under one roof. Legendary, the powerhouse behind the Dune series and the upcoming Minecraft movie, would combine its production muscle with Lionsgate’s massive catalog, which includes heavy hitters like John Wick and The Hunger Games. This interest comes at a pivotal moment for Lionsgate Studios, which became a separately traded entity in May 2025 after splitting off from Starz. The studio currently boasts a library of over 20,000 titles and recently celebrated a historic win with the Michael Jackson biopic, which became the first biopic to cross the one billion dollar mark at the global box office.

Despite recent wins in the theater, Lionsgate continues to navigate a complex financial landscape. Recent data shows a significant jump in overall revenue alongside an improved quarterly net loss, though these gains were partially offset by declines within its television division. With substantial debt still on the books, a buyout could provide much needed stability while offering Legendary the infrastructure it needs to stop relying on outside partners to get its films into theaters.

Legendary enters these negotiations from a position of relative strength after buying out Dalian Wanda Group’s stake last year, leaving itself and Apollo Global Management in control of the business. While other industry players like Banijay and Mediawan have previously shown curiosity about acquiring Lionsgate, none have moved forward with formal bids until now. Market observers will be watching closely as Lionsgate prepares to release its latest fiscal results this coming Thursday evening, which may provide further clues on whether this high stakes gamble will finally result in a sale.

Market strategists are beginning to pivot their portfolios as the artificial intelligence boom reaches a fever pitch, opting to secure realized gains rather than riding the wave indefinitely. By selling off portions of high flying AI stocks, investors are effectively locking in substantial profits while avoiding the potential volatility that often follows periods of parabolic growth. This move signals a transition toward a more balanced approach, treating the tech surge as a successful harvest rather than a permanent trajectory.

At the same time, caution is mounting within the financial sector, leading many to reduce their exposure to banks heavily tied to commercial credit markets. The decision to trim these positions reflects growing anxiety over loan defaults and the lingering stress of higher interest rates on corporate borrowers. As credit risks become more pronounced, shifting capital away from exposed lenders serves as a defensive hedge against possible instability in the banking system.

This dual strategy highlights a broader trend of risk management in today’s unpredictable economic climate. By capturing wins in the semiconductor and software spaces while distancing themselves from fragile credit lines, traders are attempting to protect their wealth without completely exiting the market. It is a calculated dance between greed and fear, prioritizing liquidity and safety over speculative long term holds during a period of structural shift.

For several seasons now, the real drama surrounding Netflix hasn’t been on the screen, but in its financial reports. Between corporate layoffs, executive turnover, and a stock price that has plummeted nearly fifty percent from its peak, investors have grown accustomed to a cycle of quarterly disappointments. However, as the streaming giant prepares to release its latest earnings figures, there are signs that the market is finally ready to stop rooting against the company.

Options traders are placing significant bets that the downward spiral is reaching its conclusion. Current pricing suggests a nine percent swing following the announcement, marking the highest expected volatility since late 2022. While previous quarters saw cautious hesitation, current activity shows a distinct shift toward optimism. Call options are being snapped up at a rate far outpacing put options, signaling that many believe the worst is behind them.

The level of conviction among some big players is particularly striking. One massive trade involved selling millions of dollars in put options right at the money, essentially acting as a high stakes vote of confidence in the stock’s stability. Even bolder speculators are buying deep out of the money calls that would require a twenty percent surge by Friday just to break even. Whether these gambles pay off remains to be seen, but for once, traders seem convinced that Netflix is due for a comeback story.